Milestone — A DevSecOps Pipeline in the SDLC
A basic DevSecOps process across the SDLC for a Java web app, driven by Jenkins.
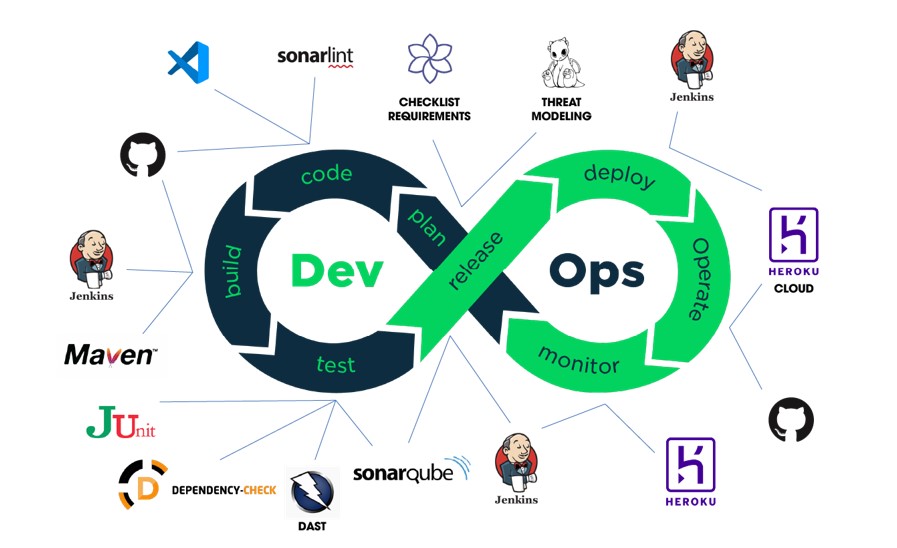
This project describes basic DevSecOps process in SDLC cycle with basic Java Web Application. This project use Jenkins to integrations all of stages. You can view demo here!
About Milestone DevSecOps cycle
I use Jenkins for through out the process and all job is handled on it.
Plan & Analysist Stages
- Prepare the checklist with Security Knowledge Framework
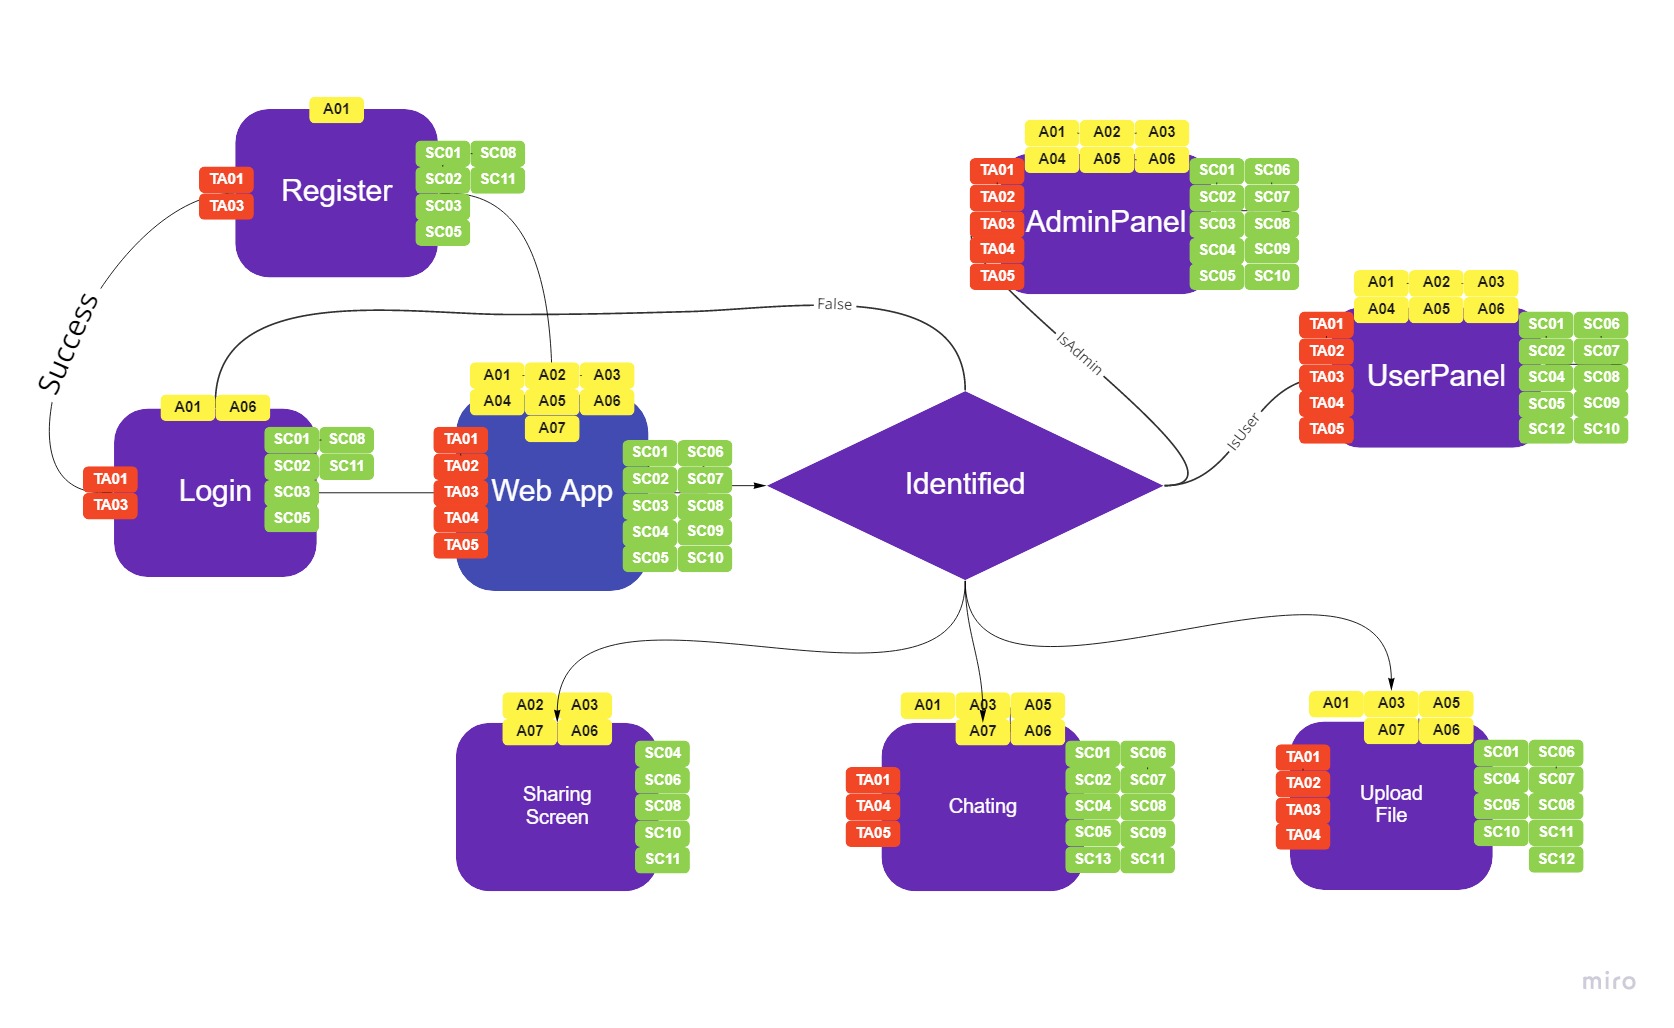
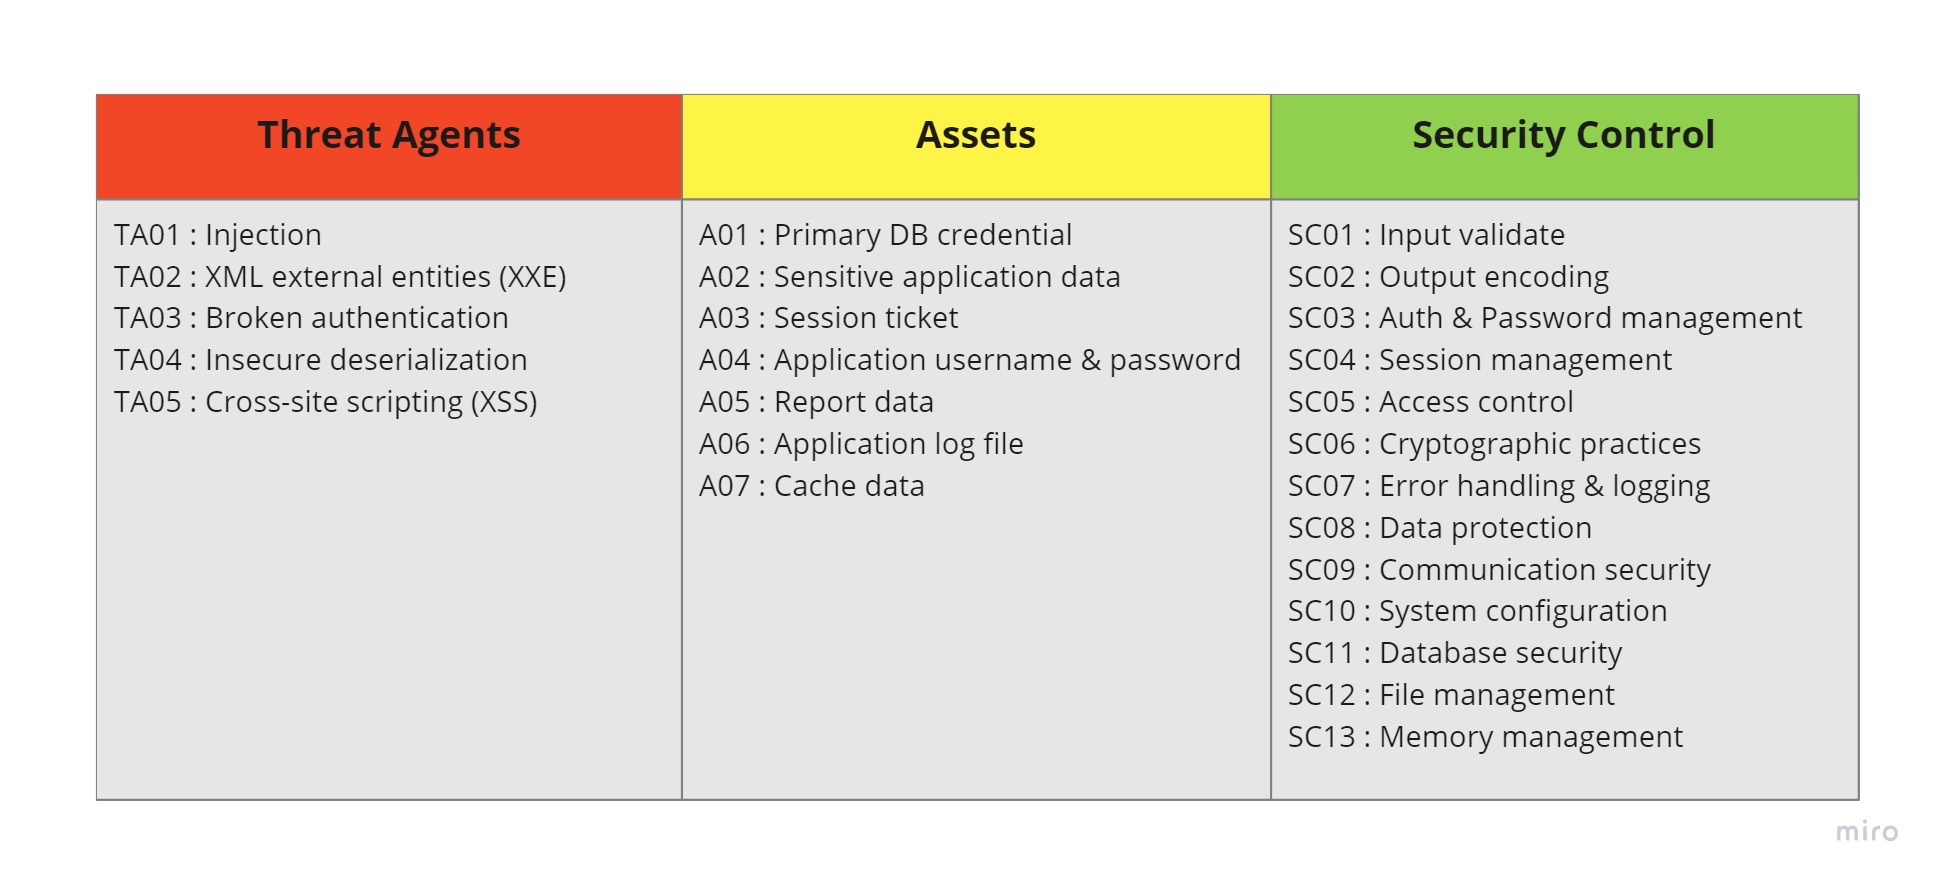
- Value security & risk of blueprint using Miro App to design threat modeling
Coding Stage
I use:
- VS Code: IDE for dev
- SonarLint: Application of Sonar ecosystem to improve code quality, code pattern and security code
- Github: Store & archive sources, prepare for next stage
- Maven: Build java project
Test & Scan Stages
In this stage, I will use 2 type of scanning - SAST & DAST scan for this project:
- SAST (Static Application Security Testing): OWASP Dependency-Check and SonarQube scan
- DAST (Dynamic Application Security Testing): OWASP ZAP Proxy
Release & Deploy Stages
- Jenkins Tool
- Heroku Cloud: for web app deploy and monitoring
Threat Modeling